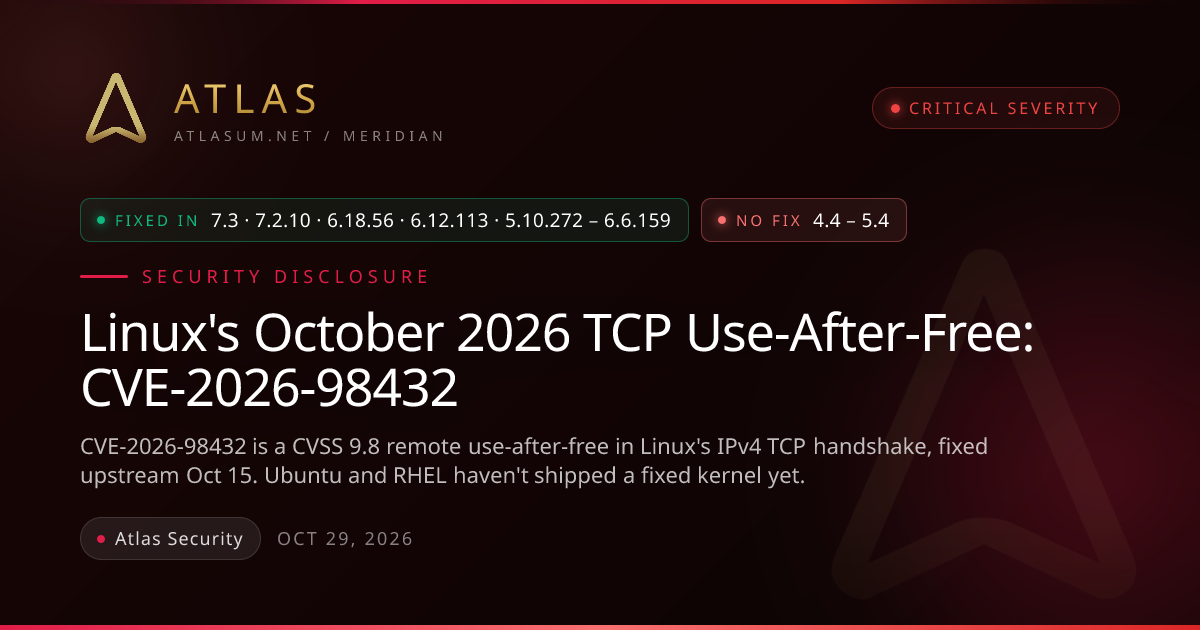
A critical use-after-free vulnerability in the Linux kernel's IPv4 TCP handshake, tracked as CVE-2026-98432, carries a CVSS 9.8 severity rating and can be triggered remotely by an unauthenticated peer. The Linux kernel CNA published the score, and upstream stable releases fixed the flaw on October 11 and 15, 2026. The bug dates back to Linux 4.4.
The problem sits in code every Linux server runs when it accepts an IPv4 TCP connection, before any application sees the traffic. Anthropic, whose researcher reported the bug, says its Claude model produced a working proof-of-concept exploit that runs commands as root on Linux servers with a multipath TCP listener, without credentials. As of October 29, Ubuntu and Red Hat had not shipped fixed kernels.
Fixed Linux kernel versions
The upstream fix, a four-line change in the handshake path, landed in these stable releases. Systems running older kernels on the 4.4 through 7.2 lines remain exposed until they move to a patched build or apply a distribution fix.
- 5.10.272
- 5.15.223
- 6.1.190
- 6.6.159
- 6.12.113
- 6.18.56