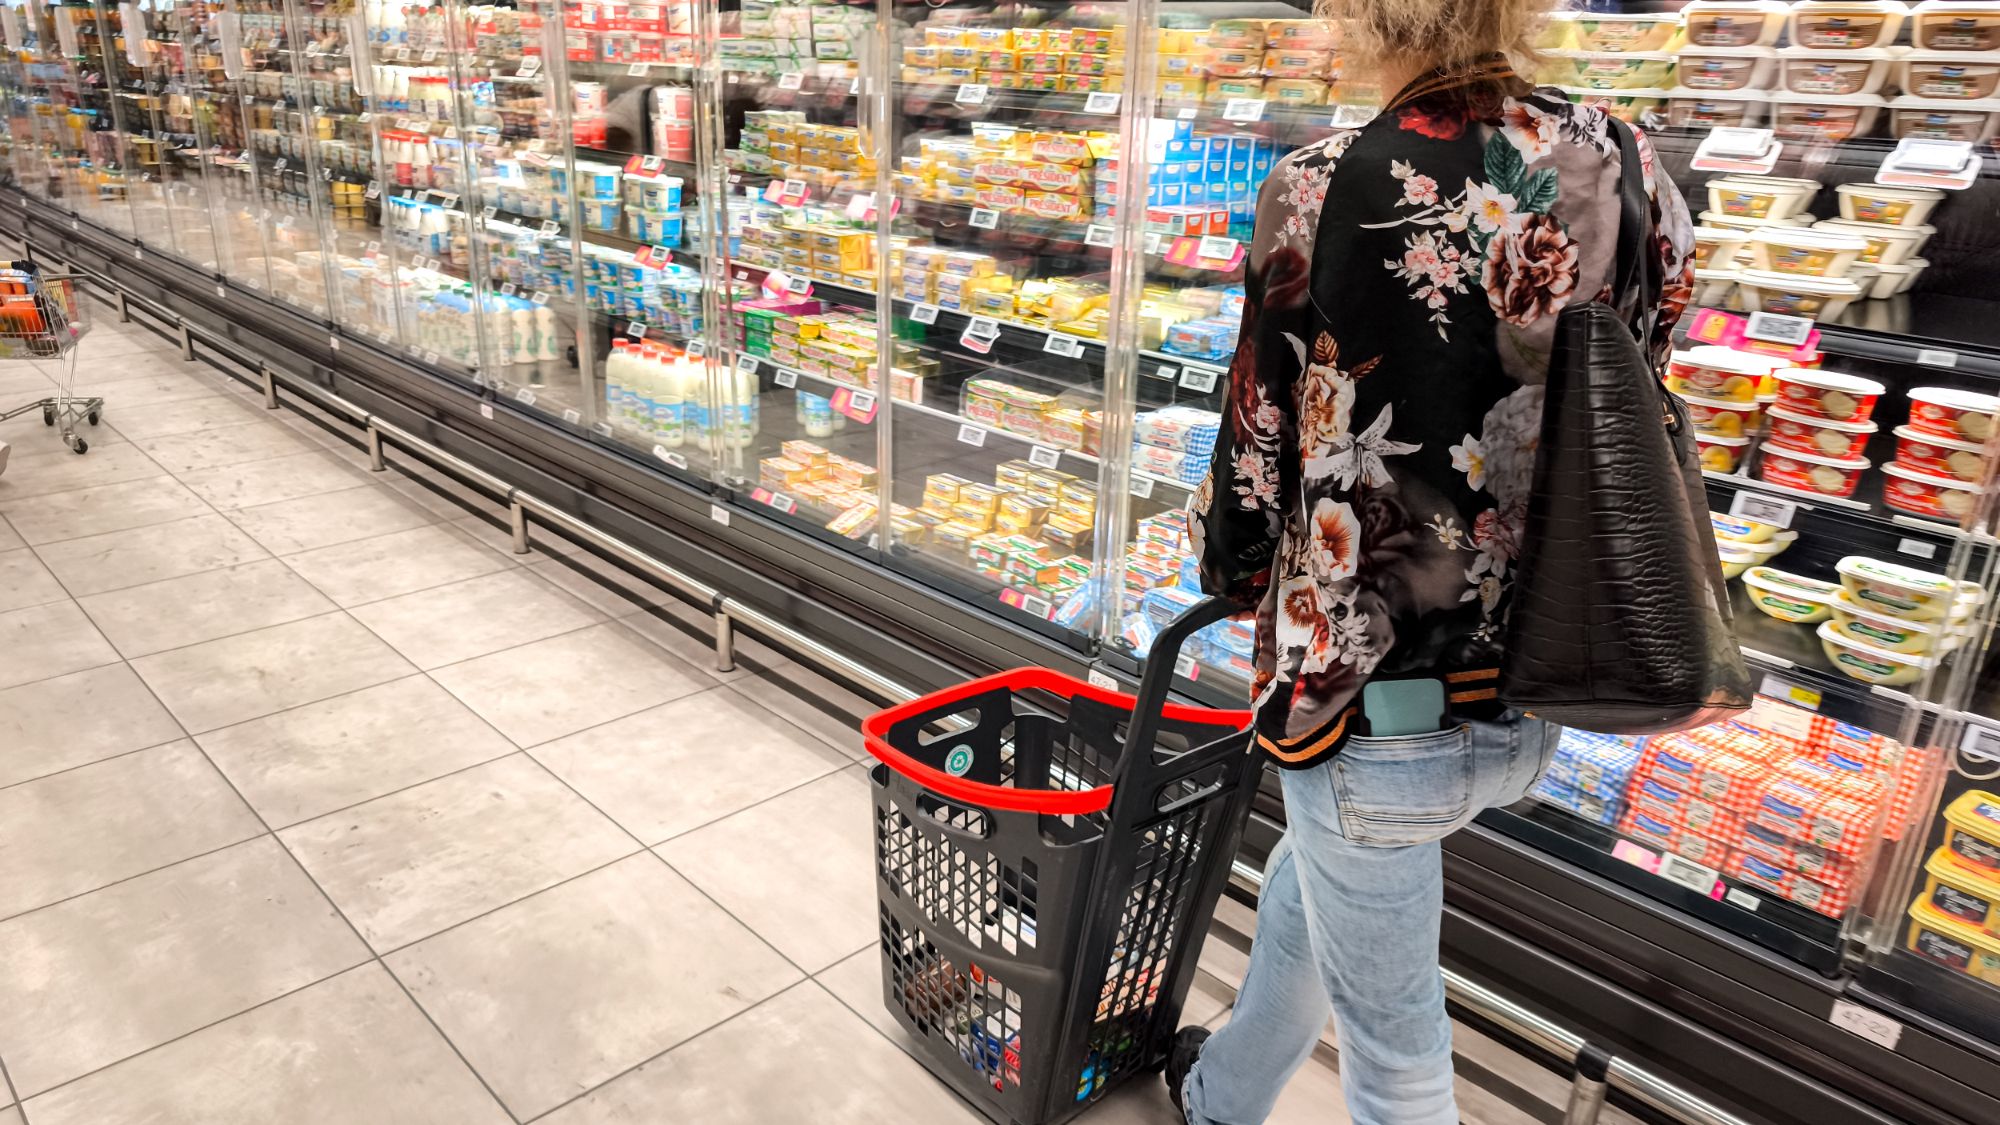
A cyberattack has struck supermarket refrigeration systems in Europe, with attackers reportedly forcing units into automatic defrost mode and disabling cold storage in stores, according to Tom's Hardware. The incident affected hundreds of fridges, turning connected cooling equipment into the entry point of a retail disruption rather than a data breach.
The timing and the exact list of affected chains have not been confirmed in the report. What is clear is that the attack was remote: no physical access to the stores was required, which is precisely what makes connected retail hardware a growing security concern for the industry.
What the Europe fridge cyberattack actually did
According to Tom's Hardware, the hackers activated the automatic defrost cycle on impacted units. Defrosting is a normal, scheduled function on commercial fridges, but running it continuously or out of cycle warms the cabinet and puts perishable goods at risk.
Because the affected equipment was network-connected, the attackers could trigger that mode from outside the store. That distinguishes this incident from a power cut or a mechanical failure: the fridges were working as designed, just under someone else's control.
- Target: supermarket refrigeration units across Europe
- Method: remote activation of automatic defrost mode
- Reported impact: fridges disabled, cold chain at risk
- Source: Tom's Hardware