A security scare has hit the JavaScript and TypeScript world: developers are reporting that a Zod release, specifically version 4.6.6, may have been compromised by malware. The Zod library is a schema validation tool maintained by colinhacks on GitHub, used for static type inference across countless TypeScript projects, apps and backend services.
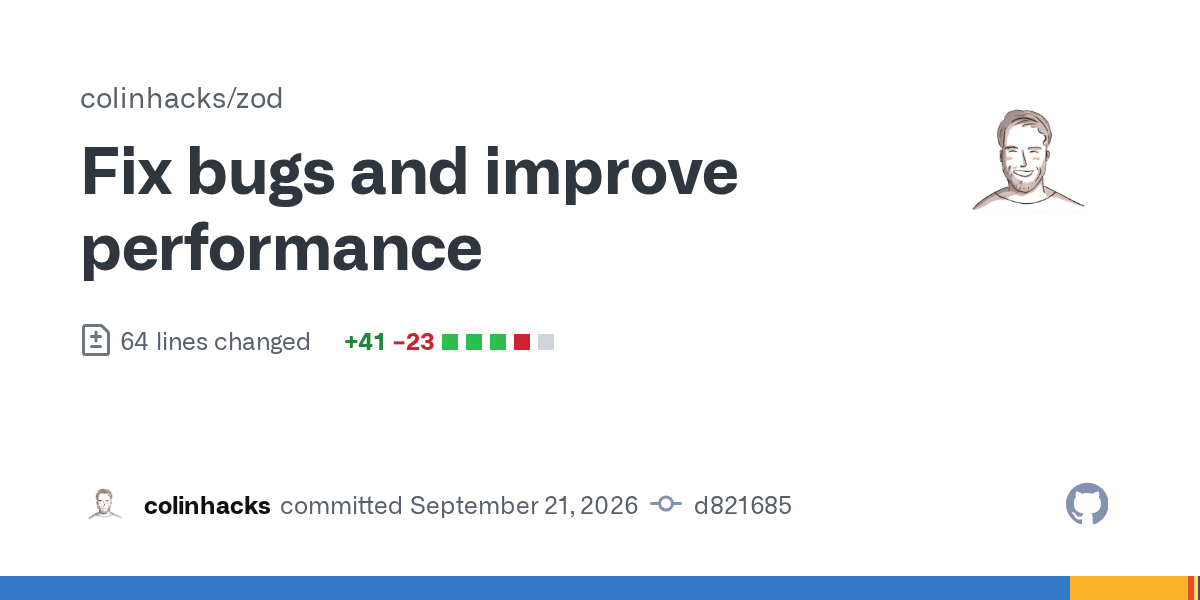
The concern surfaced in the repository's own activity, where a commit described as fixing bugs and improving performance (d821685) drew suspicion from the community. For now, this remains a reported compromise rather than a fully confirmed incident, and the exact scope of what was altered has not been established in the material we reviewed.
Zod 4.6.6 compromise: what we know
Zod is not a niche utility. It sits inside validation layers, API contracts and form handling code in a very large number of TypeScript codebases, which is why a single suspicious release spreads alarm quickly. If malicious code lands in a dependency this widely used, it can reach production systems, CI pipelines and developer machines without anyone reviewing a line of it.
The details circulating so far are thin. There is no confirmed list of affected versions beyond reports naming 4.6.6, no confirmed description of the payload, and no official advisory cited in the sources we saw. Treat every claim about specific behaviour as unverified until the maintainer or a security body publishes a statement.
- Zod is a TypeScript-first schema validation library with static type inference
- The version flagged in reports is Zod 4.6.6
- The maintainer is colinhacks on GitHub